Content ITV PRO
This is Itvedant Content department
Implement Event Correlation to Identify a Complex Security Incident
Business Scenario
Welcome!
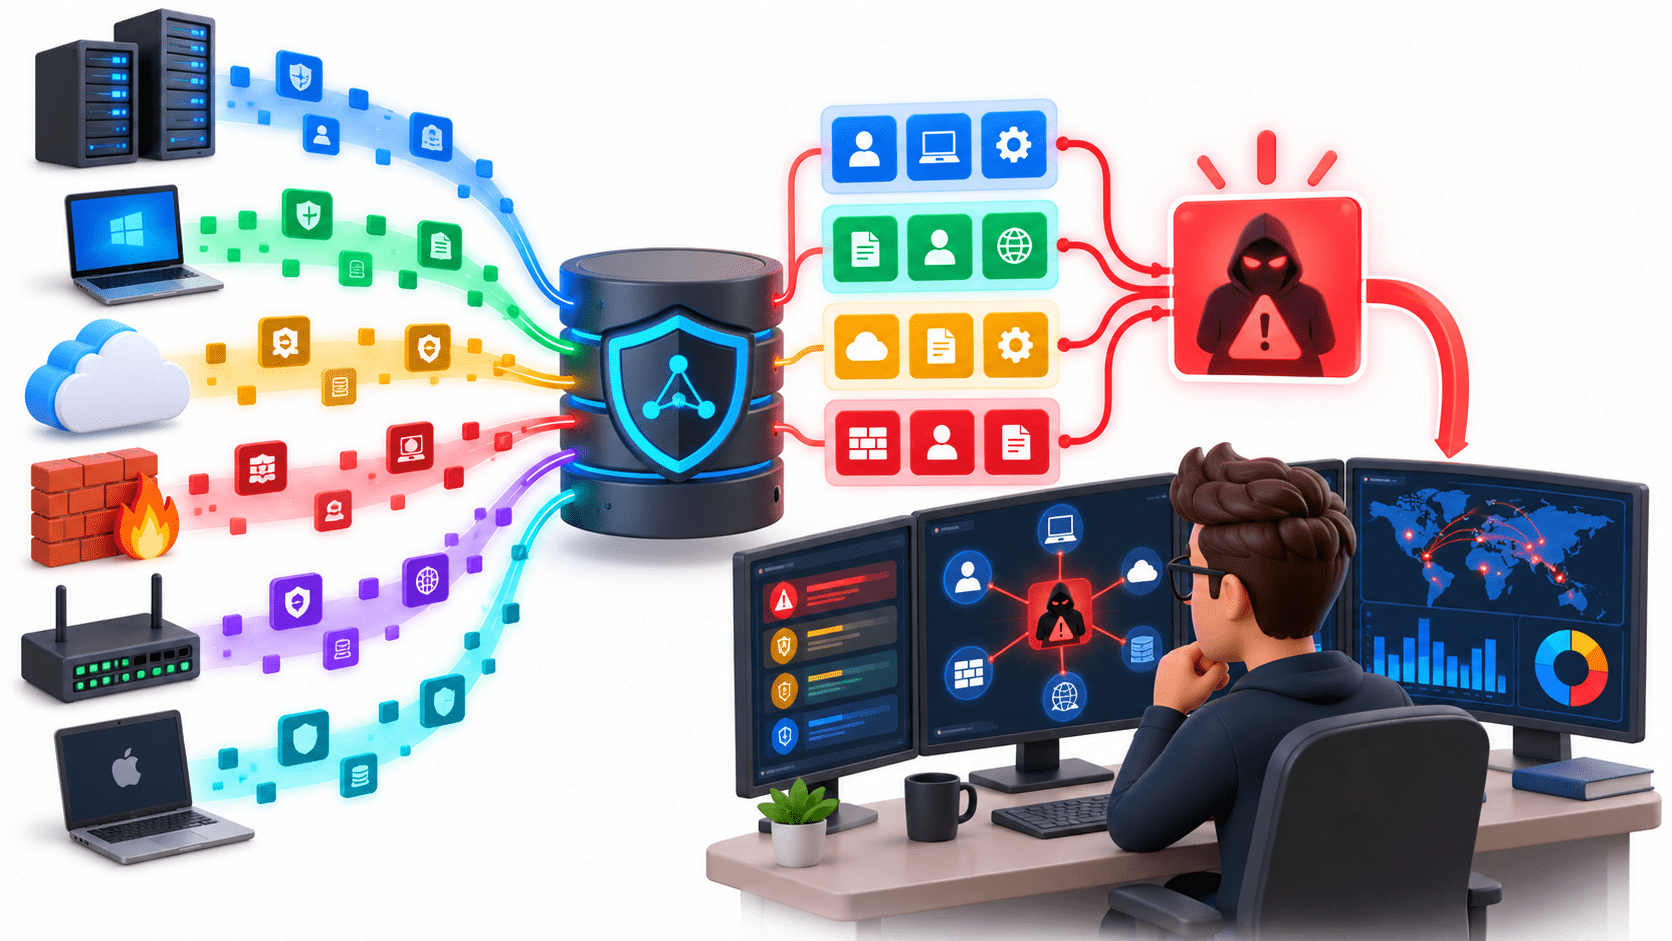
You are a SOC Analyst at CyberSecure Solutions. The SIEM is receiving thousands of events from different systems. Individually, many events appear harmless, but when several related events occur together, they may indicate a security incident.
Your task is to create a basic correlation rule, generate controlled security events, and use the SIEM to identify a simulated complex incident.
Pre-Lab Preparation
Topic : SIEM and Security Frameworks
1) SIEM concepts and architecture
2) Incident response lifecycle
3) MITRE ATT&CK framework overview
Task 1: Understand Event Correlation
Understand why multiple events need to be analyzed together.
1
Steps
a
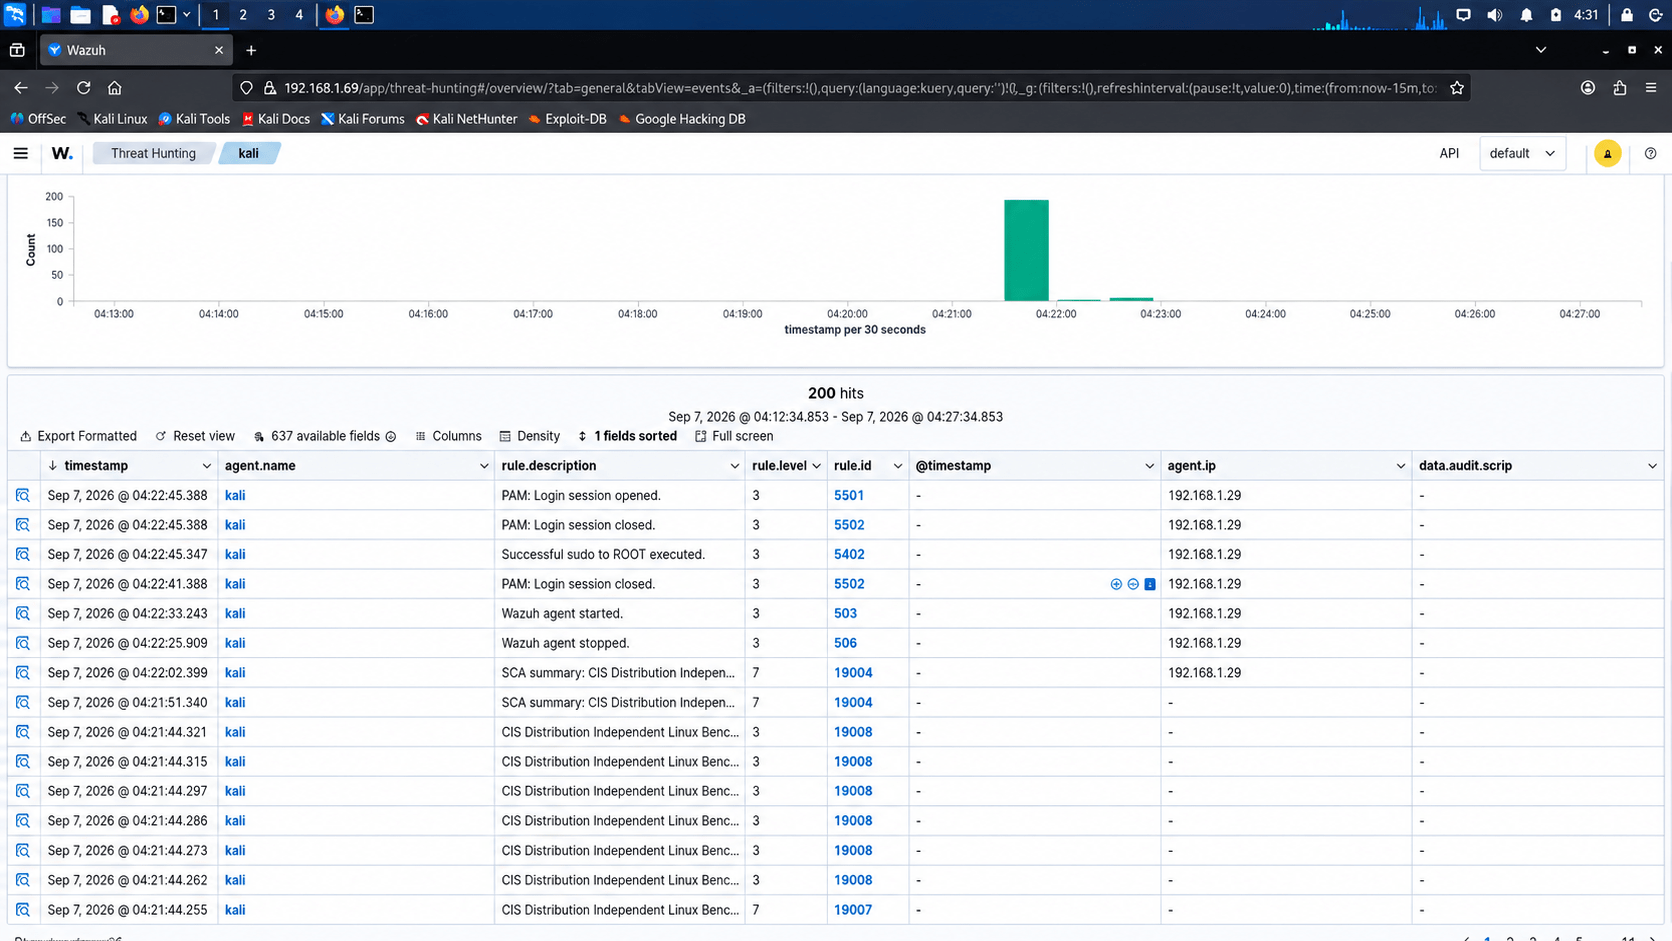
Open the SIEM dashboard.
Review individual security events.
Identify events that occur close together in time.
Compare their:
Source IP
Username
Host
Timestamp
Event type
Identify whether the events could be related.
Open the SIEM dashboard.
Review individual security events.
Identify events that occur close together in time.
Compare their:
Source IP
Username
Host
Timestamp
Event type
Identify whether the events could be related.
Task 2: Create a Correlation Rule
Create a simple rule that detects a sequence of related events.
1
Steps
a
Open the SIEM rule/correlation configuration.
Define the first event:
Multiple failed login attempts.
Define the second event:
Successful login from the same source/user.
Define the third event:
Privileged or sensitive activity.
Set a suitable time window.
Configure the SIEM to generate a higher-severity alert when the events occur together.
Save the rule.
Example Scenario
Detect:
Multiple failed logins → successful login → privileged activity
Open the SIEM rule/correlation configuration.
Define the first event:
Multiple failed login attempts.
Define the second event:
Successful login from the same source/user.
Define the third event:
Privileged or sensitive activity.
Set a suitable time window.
Configure the SIEM to generate a higher-severity alert when the events occur together.
Save the rule.
<group name="soc_lab_correlation,">

  <!-- Failed SSH authentication -->
  <rule id="100300" level="4">
    <if_sid>5716</if_sid>
    <description>SOC Lab: Failed SSH login detected.</description>
    <group>soc_lab_sequence,</group>
  </rule>

  <!-- Successful SSH authentication -->
  <rule id="100301" level="4">
    <if_sid>5715</if_sid>
    <description>SOC Lab: Successful SSH login detected.</description>
    <group>soc_lab_sequence,</group>
  </rule>

  <!-- Privileged sudo activity -->
  <rule id="100302" level="5">
    <program_name>sudo</program_name>
    <description>SOC Lab: Privileged sudo activity detected.</description>
    <group>soc_lab_sequence,</group>
  </rule>

  <!-- Correlation: five related events within five minutes -->
  <rule id="100303" level="14" frequency="5" timeframe="300">
    <if_matched_group>soc_lab_sequence</if_matched_group>
    <description>SOC Lab CORRELATED INCIDENT: Multiple related
    authentication and privileged events detected.</description>
    <group>soc_lab_correlated_incident,</group>
  </rule>

</group>
<group name="soc_lab_correlation,">
<!-- Failed SSH authentication -->
<rule id="100300" level="4">
<if_sid>5716</if_sid>
<description>SOC Lab: Failed SSH login detected.</description>
<group>soc_lab_sequence,</group>
</rule>
<!-- Successful SSH authentication -->
<rule id="100301" level="4">
<if_sid>5715</if_sid>
<description>SOC Lab: Successful SSH login detected.</description>
<group>soc_lab_sequence,</group>
</rule>
<!-- Privileged sudo activity -->
<rule id="100302" level="5">
<program_name>sudo</program_name>
<description>SOC Lab: Privileged sudo activity detected.</description>
<group>soc_lab_sequence,</group>
</rule>
<!-- Correlation: five related events within five minutes -->
<rule id="100303" level="14" frequency="5" timeframe="300">
<if_matched_group>soc_lab_sequence</if_matched_group>
<description>SOC Lab CORRELATED INCIDENT: Multiple related
authentication and privileged events detected.</description>
<group>soc_lab_correlated_incident,</group>
</rule>
</group>Task 3: Generate Controlled Events
Generate events that match the correlation rule.
1
Steps
a
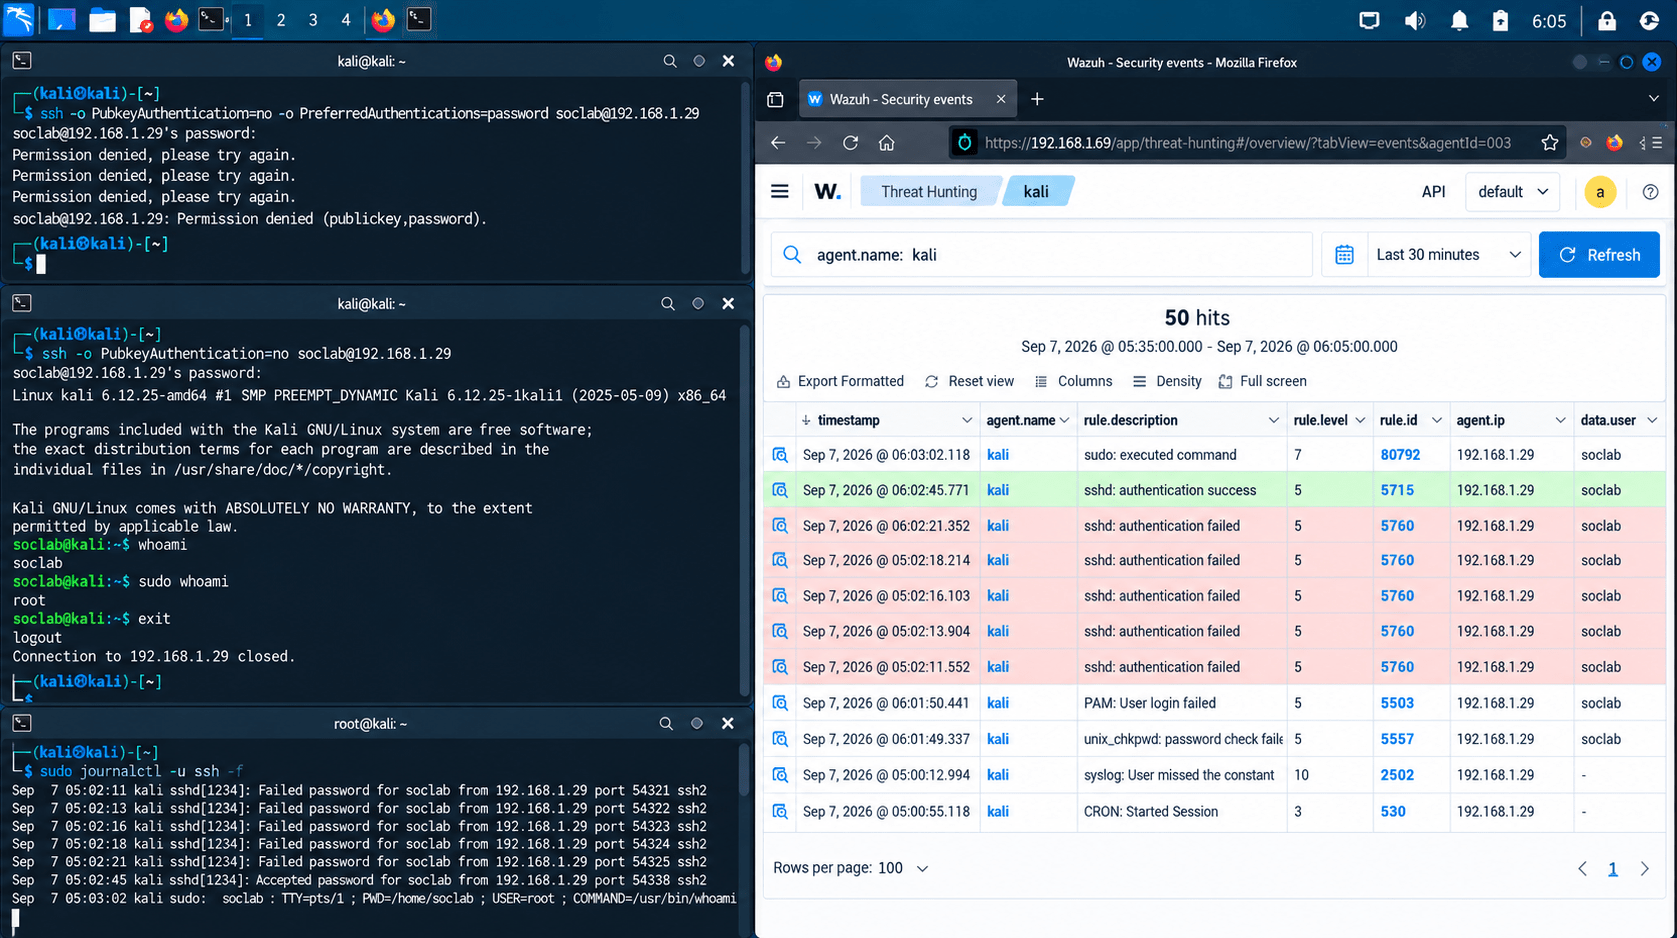
Use the authorized test account.
Generate several incorrect login attempts.
Perform a successful login.
Perform an approved privileged test action.
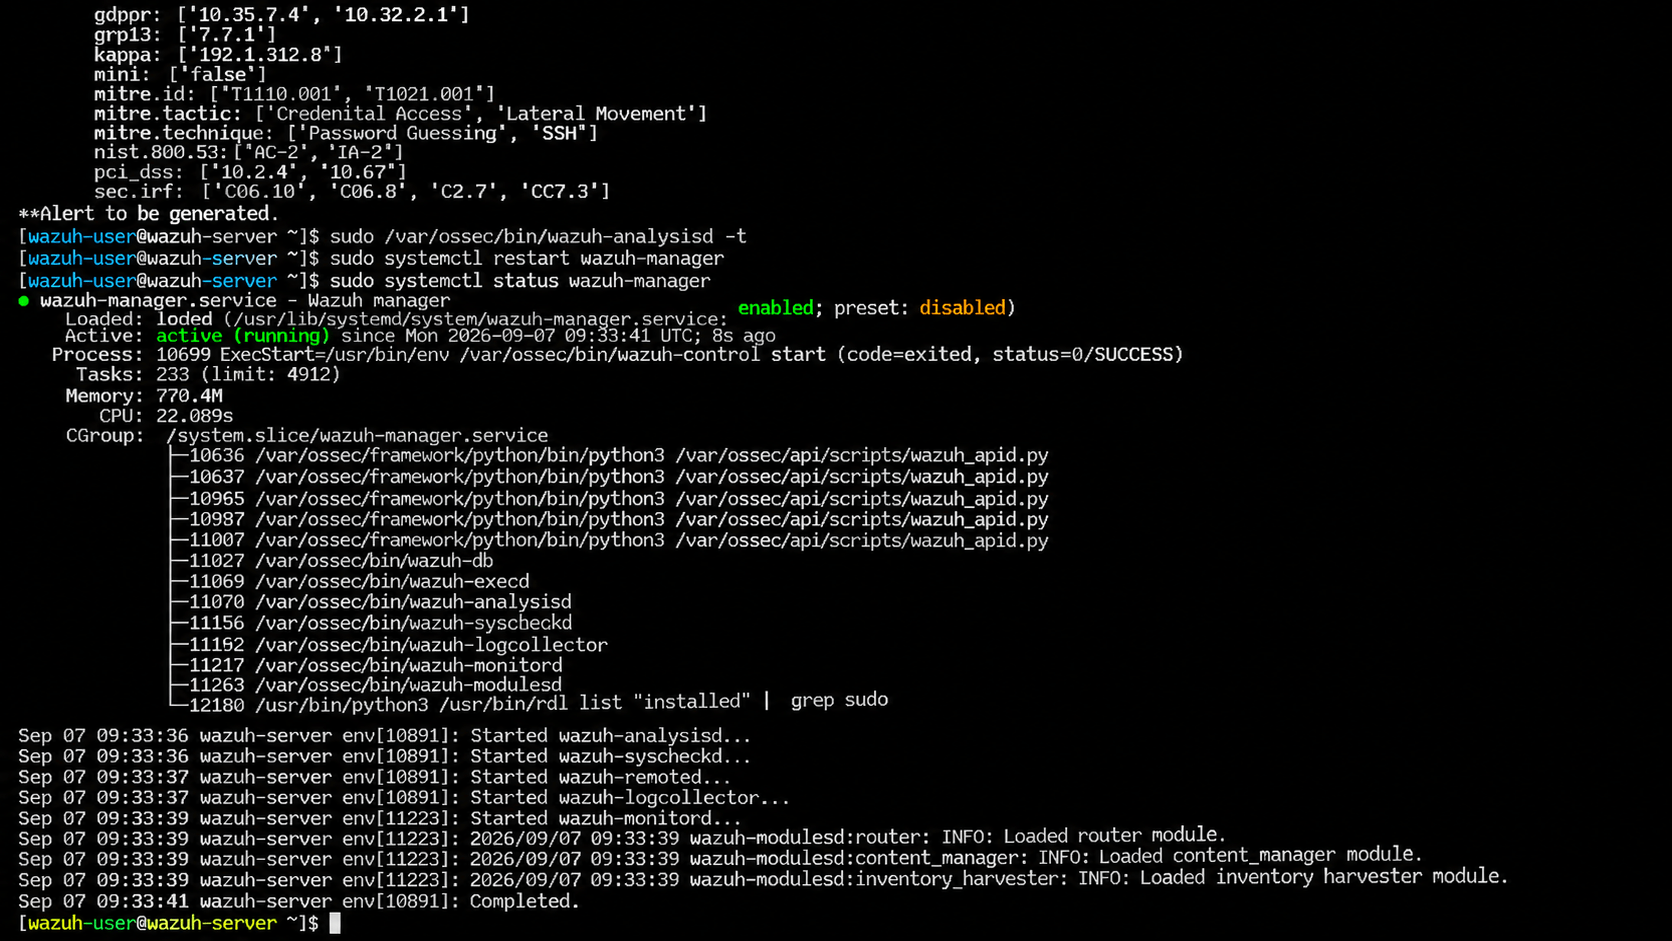
Monitor the SIEM.
Wait for the correlation rule to trigger.
Use the authorized test account.
Generate several incorrect login attempts.
Perform a successful login.
Perform an approved privileged test action.
Monitor the SIEM.
Wait for the correlation rule to trigger.
Task 4: Investigate the Correlated Alert
Task 1: Understanding BRD
Before you start building anything, you need to clearly understand what the client actually wants.So, let’s begin by understanding the BRD (Business Requirement Document) shared by the client.
BRD Full Form is Business Requirement Details.BRD like a plan for building a house. This plan helps the builder understand what to build.In the same way,BRD tells developers what the client wants to build
Click to download BRD : BiteBox_BRD.pdf
Activity
After going through BRD list down the Core Features and Web Pages in the tabulated Format as shown Below.
| Col 1 | Col 2 | Col 3 |
|---|---|---|
| Row 1 | ||
| Row 2 | ||
| Row 3 |
Formula
Profit = Revenue - Cost
Task 2: Create WireFrame
Now that you understand the requirements, don’t jump into coding yet. Before development, we always visualize the layout.
Now lets create a simple wireframe for the homepage.
A wireframe is like a layout plan of a house. Before building, you decide where rooms, doors, and windows will be placed.Similarly, a wireframe helps you plan where elements like headers, images, and buttons will appear on a webpage—before adding design or colours.
Task 3: Code Editor Installation
Good work on completing the planning phase.
Now we will start development. Before that, make sure your system is ready with the required tools.
In this step we will install the VS code editor that will help to Write code efficiently,Organize files , Run and test your application
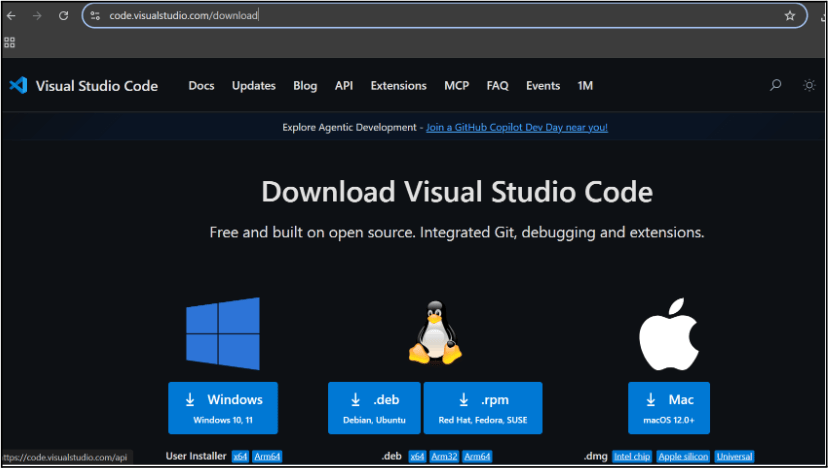
Go to the visual studio code official website
1
Click to download Homepage Wireframe : Homepage Wireframe
Choose your operating system(windows / Mac) and download the installation file.
Double click on the download app and Accept the agreement and click next
2
It is a long established fact that a reader will be distracted
b
Sub Steps
a
Double click on the download app and Accept the agreement and click next
public class MathSample {
    public static void main(String[] args) {
        int x = 10;
        int y = 20;
        int sum = x + y;

        System.out.println("The sum is: " + sum);
    }
}
public class MathSample {
public static void main(String[] args) {
int x = 10;
int y = 20;
int sum = x + y;
System.out.println("The sum is: " + sum);
}
}
public class MathSample {
public static void main(String[] args) {
int x = 10;
int y = 20;
int sum = x + y;
System.out.println("The sum is: " + sum);
}
}
Great job!
You have successfully completed your first lab on BiteBox Project Onboarding.
In this lab, you have: Understood the BRD, Created a wireframe, Set up your development environment, Organised your project structure, Run your first program
You are now ready to move to the next stage of development
Checkpoint
Next-Lab Preparation
Git Push
git push origin branchNameTopic : Working with a Text and Listin HTML
1) Power of HTML text tags
2) Customizing your style with CSS
3) Listing it right using HTML
4) HTML Link up , attributes of tag, block vs inline elements
Text box Width : 887
Business Scenario, Pre-lab Preparation, Next-lab Preparation, Task, Activity, Checkpoint : 90%.
Steps : 1,2,3 [Sub Steps - a,b,c]
Normal Text, Topic Name : 80%
Subtopic : 70%
Code Box font Size : 16px
By Content ITV